Cronus
I love contributing to a safer Cyber Security Ecosystem
through
Offensive Security Research

My Github


HackfestCTF 2024 Web writeup
·
🚩 CTF
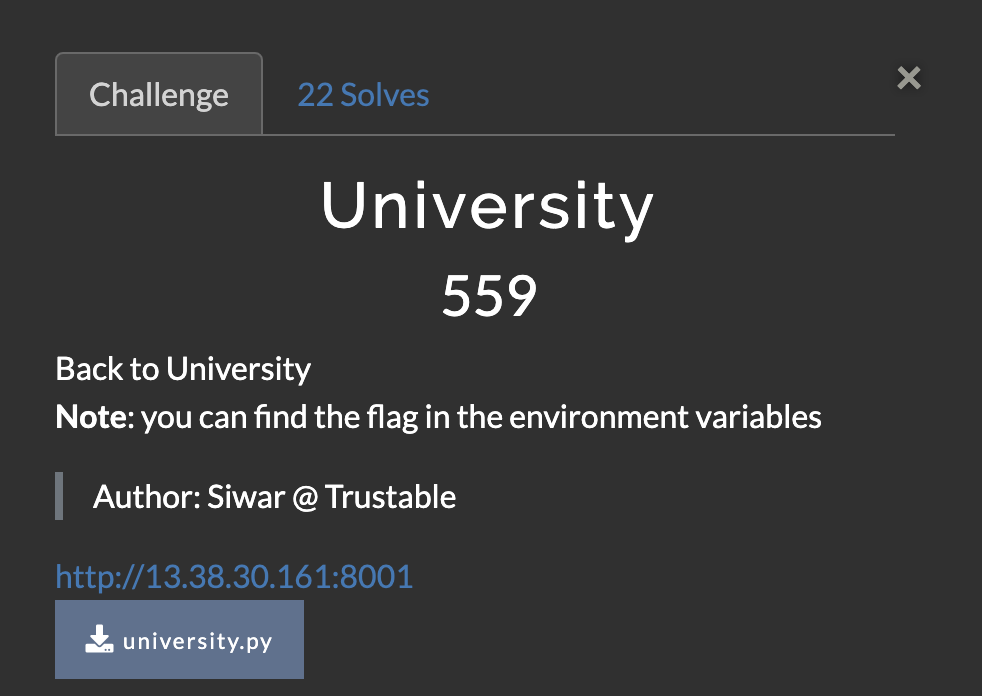
[ University ] We need to access to environment variable. @app.route('/', methods=['GET', 'POST']) def login(): if request.method == 'POST': username = request.form['username'] password = request.form['password'] try: response = requests.get(f"http://localhost:5000/api/users/{username}/auth") response.raise_for_status() conn = connect_db() cursor = conn.cursor() cursor.execute('SELECT * FROM use..
damCTF 2024 Web Writeup
·
🚩 CTF
My team was too good for me to help, but here's a writeup I did on my own for studying purposes. Flower Power # app.py ... @dataclass class Flower: name: str flower_url: str description: str id: str = "-1" database: dict[str, Flower] = dict() def add_flower(flower: Flower): flower.id = generate_id() database[flower.id] = flower return flower add_flower(Flower( "Rose", "https://i0.wp.com/pikespea..
Phar Deserialization
·
WEB
Serialization & DeserializationSerialization : 데이터 구조체나 Object 상태의 데이터를 다른 시스템 환경에서도 해석될 수 있도록 Byte Stream 상태로 변환하는 과정Deserialization : Byte Stream 상태의 데이터를 데이터 구조체나 Object로 변환하는 과정Phar (PHP Archive)Phar는 내부에 실행 가능한 PHP 코드를 모아놓은 아카이브 포맷을 뜻한다. Phar 파일은 아래 4가지의 구조로 이루어진다.StubManifestFile ContentsSiganutre (Optional)[ Stub ]Stub은 작은 형태의 코드를 담을 수 있는 공간이다. Stub의 마지막 명령어에는 반드시 _HALTCOMPILER()가 포함되어야 한..
CVE-2024-4367 (PDF.js - Arbitrary JS Execution)
·
💻 Security
Vulnerable Product & VersionAll FireFox Users ( Services which use pdfjs-dist(SummaryPDF.js acts as a viewer to show a preview of a pdf file, which is made by Mozila.It has the ability to render fonts and CVE-2024-4367 vulnerabilitiy targets this part.The user can set the values of the PDF file's properties, and pdf.js applies them by executing JavaScript code.However, there is no validation of ..
CodeQL 사용법 (이론편)
·
Tips
[ 들어가기에 앞서.. ]CodeQL 사용법에 대한 적절한 레퍼런스가 따로 없어, 익히는 데에 애를 많이 먹었다. 남들은 삽질을 덜 했으면 좋겠다는 생각에 정리한다. [ Intro ]CodeQL은 Variant Analysis를 수행하는 정적 분석 도구이다. CodeQL에서는 code를 데이터 취급하며, 취약점을 포함한 버그 채턴들을 code로부터 만들어낸 DB에서 실행할 수 있는 쿼리로 정형화해서 이용한다.Variant Analysis란 알려진 취약점을 기준 삼아 비슷한 유형의 취약점을 찾아내는 분석 방법이다. CodeQL은 취약점을 쿼리화할 수 있어 Variant Analysis 분석에 효율적이다. 또한 새로운 유형의 취약점을 찾기 위해 직접 쿼리화할 수 있다. [ Internal ]CodeQL이 내..
[ Bug Report ] Success to exploit Skype (feat. RCE, pyzw file)
·
Bug Report
• Executive SummaryI have recently discovered a critical Remote Code Execution (RCE) vulnerability in Skype. This bug presents a severe security risk as it enables an attacker to potentially take control of a victim's computer. Although this finding did not result in a reward or a CVE identification, it has been acknowledged as valid by Microsoft's security team, and I wish to document it for re..